#[derive(Accounts)]
pub struct Withdraw<'info> {
    #[account(mut, has_one = authority)]
    pub vault: Account<'info, Vault>,
    pub authority: Signer<'info>,
    #[account(mut)]
    pub recipient: SystemAccount<'info>,
}

pub fn withdraw(ctx: Context<Withdraw>, amount: u64) -> Result<()> {
    let vault = &mut ctx.accounts.vault;
    require!(amount <= vault.balance, VaultError::Insufficient);
    // invariant: total_shares * price == balance
    vault.balance = vault.balance.checked_sub(amount).ok_or(VaultError::Overflow)?;
    vault.total_shares = vault.shares_for(vault.balance)?;
    Ok(())
}fn verify_commit(&self, commit: &Commit, vals: &ValidatorSet) -> Result<(), ConsensusError> {
ensure!(commit.height == self.height, ConsensusError::WrongHeight);
let mut seen = HashSet::new();
let mut power: u64 = 0;
for vote in &commit.votes {
// invariant: at most one vote per validator per round
ensure!(seen.insert(vote.validator), ConsensusError::DuplicateVote);
let val = vals.get(&vote.validator).ok_or(ConsensusError::UnknownValidator)?;
val.pub_key.verify(&commit.sign_bytes(vote.round), &vote.signature)?;
power = power.checked_add(val.voting_power).ok_or(ConsensusError::Overflow)?;
}
// assumption: more than 2/3 of the voting power is honest
ensure!(power as u128 * 3 > vals.total_power() as u128 * 2, ConsensusError::NoQuorum);
Ok(())
}func (k Keeper) Delegate(ctx sdk.Context, del sdk.AccAddress, amt math.Int) error {
if amt.IsNegative() { return ErrInvalidAmount }
val, found := k.GetValidator(ctx, del)
if !found { return ErrNoValidator }
// assumption: unbonding queue is bounded per block
return k.bank.DelegateCoins(ctx, del, types.BondedPool, sdk.NewCoins(sdk.NewCoin(k.BondDenom(ctx), amt)))
}pub fn execute_inbound(deps: DepsMut, msg: InboundMessage, proof: Proof) -> Result<Response, BridgeError> {
// assumption: relayers may be malicious, only the light client is trusted
let root = LIGHT_CLIENT.load(deps.storage)?.verified_root(msg.source_height)?;
ensure!(proof.verify(&root, &msg.hash()), BridgeError::InvalidProof);
let expected = NONCES.may_load(deps.storage, &msg.channel)?.unwrap_or(0);
// invariant: every message executes exactly once, in order
ensure!(msg.nonce == expected, BridgeError::NonceMismatch { expected, got: msg.nonce });
NONCES.save(deps.storage, &msg.channel, &(expected + 1))?;
Ok(Response::new().add_message(msg.into_cosmos_msg()?))
}function liquidate(address user, uint256 repay) external nonReentrant {
uint256 hf = healthFactor(user);
require(hf < 1e18, "healthy");
uint256 seized = repay * price(debt) / price(collateral) * bonus / 1e4;
_transferCollateral(user, msg.sender, seized);
}#[pallet::call_index(0)]
pub fn transfer(origin: OriginFor<T>, dest: T::AccountId, value: BalanceOf<T>) -> DispatchResult {
let who = ensure_signed(origin)?;
ensure!(who != dest, Error::<T>::SelfTransfer);
// invariant: total issuance is unchanged by transfers
T::Currency::transfer(&who, &dest, value, ExistenceRequirement::KeepAlive)
}#[derive(Accounts)]
pub struct Withdraw<'info> {
#[account(mut, has_one = authority)]
pub vault: Account<'info, Vault>,
pub authority: Signer<'info>,
#[account(mut)]
pub recipient: SystemAccount<'info>,
}
pub fn withdraw(ctx: Context<Withdraw>, amount: u64) -> Result<()> {
let vault = &mut ctx.accounts.vault;
require!(amount <= vault.balance, VaultError::Insufficient);
// invariant: total_shares * price == balance
vault.balance = vault.balance.checked_sub(amount).ok_or(VaultError::Overflow)?;
vault.total_shares = vault.shares_for(vault.balance)?;
Ok(())
}fn verify_commit(&self, commit: &Commit, vals: &ValidatorSet) -> Result<(), ConsensusError> {
ensure!(commit.height == self.height, ConsensusError::WrongHeight);
let mut seen = HashSet::new();
let mut power: u64 = 0;
for vote in &commit.votes {
// invariant: at most one vote per validator per round
ensure!(seen.insert(vote.validator), ConsensusError::DuplicateVote);
let val = vals.get(&vote.validator).ok_or(ConsensusError::UnknownValidator)?;
val.pub_key.verify(&commit.sign_bytes(vote.round), &vote.signature)?;
power = power.checked_add(val.voting_power).ok_or(ConsensusError::Overflow)?;
}
// assumption: more than 2/3 of the voting power is honest
ensure!(power as u128 * 3 > vals.total_power() as u128 * 2, ConsensusError::NoQuorum);
Ok(())
}func (k Keeper) Delegate(ctx sdk.Context, del sdk.AccAddress, amt math.Int) error {
if amt.IsNegative() { return ErrInvalidAmount }
val, found := k.GetValidator(ctx, del)
if !found { return ErrNoValidator }
// assumption: unbonding queue is bounded per block
return k.bank.DelegateCoins(ctx, del, types.BondedPool, sdk.NewCoins(sdk.NewCoin(k.BondDenom(ctx), amt)))
}pub fn execute_inbound(deps: DepsMut, msg: InboundMessage, proof: Proof) -> Result<Response, BridgeError> {
// assumption: relayers may be malicious, only the light client is trusted
let root = LIGHT_CLIENT.load(deps.storage)?.verified_root(msg.source_height)?;
ensure!(proof.verify(&root, &msg.hash()), BridgeError::InvalidProof);
let expected = NONCES.may_load(deps.storage, &msg.channel)?.unwrap_or(0);
// invariant: every message executes exactly once, in order
ensure!(msg.nonce == expected, BridgeError::NonceMismatch { expected, got: msg.nonce });
NONCES.save(deps.storage, &msg.channel, &(expected + 1))?;
Ok(Response::new().add_message(msg.into_cosmos_msg()?))
}function liquidate(address user, uint256 repay) external nonReentrant {
uint256 hf = healthFactor(user);
require(hf < 1e18, "healthy");
uint256 seized = repay * price(debt) / price(collateral) * bonus / 1e4;
_transferCollateral(user, msg.sender, seized);
}#[pallet::call_index(0)]
pub fn transfer(origin: OriginFor<T>, dest: T::AccountId, value: BalanceOf<T>) -> DispatchResult {
let who = ensure_signed(origin)?;
ensure!(who != dest, Error::<T>::SelfTransfer);
// invariant: total issuance is unchanged by transfers
T::Currency::transfer(&who, &dest, value, ExistenceRequirement::KeepAlive)
}Security Researcher — Founder & CEO, Codezen
Christian Vari.
Securingblockchain protocols.
Solana, Cosmos SDK, Polkadot SDK, Ethereum and EVM. Head of Audit Operations at Oak Security.
- Solana
- Cosmos SDK
- Polkadot SDK
- Ethereum
- EVM
- CosmWasm
- Anchor
- Substrate
- Filecoin FEVM
- Stellar
01 — About
About Christian Vari
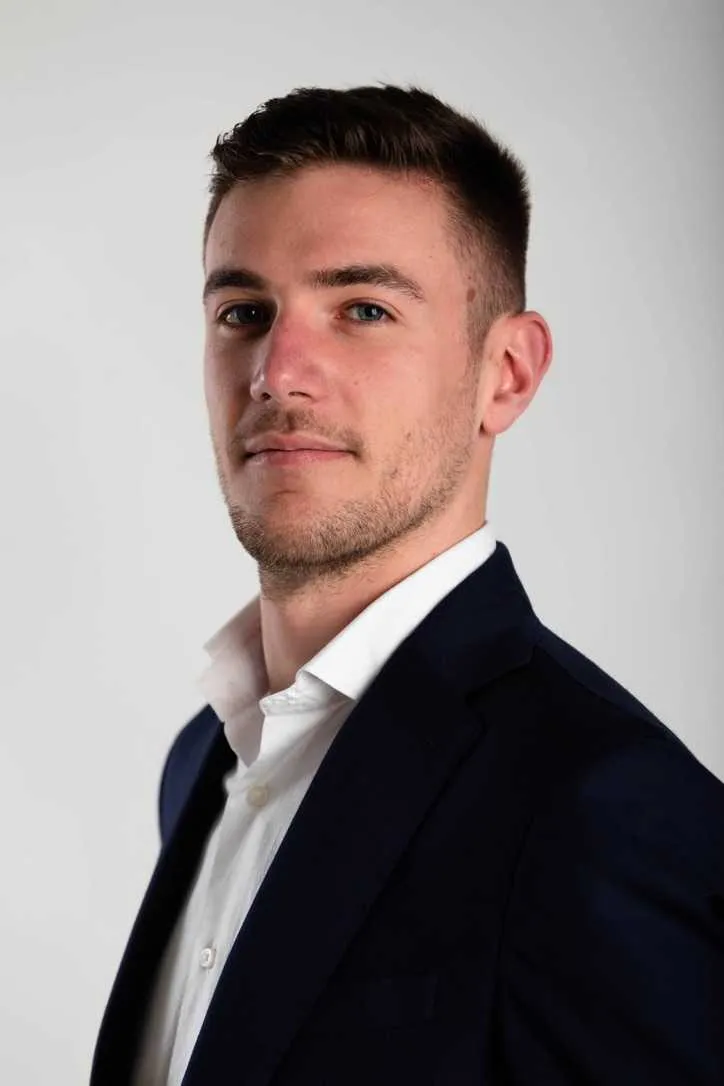
I’m Christian Vari, Founder & CEO of Codezen, a blockchain security firm focused on auditing financial and Web3 systems.
I’ve worked on 250+ audits, identifying over 900 vulnerabilities and helping securing assets across Solana, Cosmos SDK, Polkadot SDK, Ethereum and EVM ecosystems.
I currently serve as Head of Audit Operations at Oak Security and collaborate with leading security teams in the industry, including Zenith Security and Trust Security.
I’m also Chairman of Altairith Capital, a holding company focused on technology and security-driven ventures.
My work focuses on reviewing smart contracts, protocol logic, and distributed systems, with particular attention to assumptions, invariants, and real-world failure modes.
I’m particularly interested in how AI can assist security research and auditing workflows without reducing depth of reasoning or introducing new risks.
02 — Work
Experience
2018 — Now
Apr 2022 — Now
Codezen ↗
Founder, CEO and Lead Security Researcher
Management · Blockchain · Rust · Golang · Solidity · TypeScript · CosmWasm · Cosmos SDK
Sep 2025 — Now
Altairith Capital Holding ↗
Chairman
Management · Investing · Risk Management
Feb 2022 — Now
Oak Security ↗
- Head of Audit OperationsMar 2026 — Now
- Lead Security ResearcherSep 2022 — Mar 2026
- Blockchain and Smart Contract AuditorFeb 2022 — Sep 2022
Blockchain · Rust · Golang · Solidity · TypeScript · CosmWasm · Cosmos SDK · Solana · Anchor · Polkadot SDK
Jan 2025 — Now
Zenith Security ↗
Security Researcher
Blockchain · Rust · Golang · Solidity · TypeScript · CosmWasm · Cosmos SDK · Solana · Anchor · Polkadot SDK
Sep 2023 — Aug 2025
DeFi Talents @ Frankfurt School of Finance & Management ↗
Mentor
Blockchain · Finance · Management · Economy · Teaching
Apr 2020 — Aug 2022
HCL Technologies ↗
- Software Engineer IINov 2021 — Aug 2022
- Junior Software EngineerApr 2020 — Nov 2021
Virtual Reality · Microservices Architecture · NLP · Node.js · React · Python · AI · ChatBots · Scrum Master
Jan 2018 — Apr 2020
Freelance developer
Full Stack Developer
Solidity · Node.js · React · Python · C++ · C-AVR
Education
Tor Vergata University of Rome
Blockchain & Cybersecurity
Sapienza University of Rome
Software and Automation Engineering
03 — Research
Research
Patents, papers and applied research on blockchain security, smart contract auditing and AI-assisted security tooling.
04 — Expertise
Expertise
- Solana
- Anchor
- Polkadot SDK
- TypeScript
- C++
- Risk Management
Security reviews by technology
- Rust83
- Golang70
- Cosmos SDK64
- CosmWasm54
- Solidity37
- Substrate13
05 — Security reviews
Selected work
- C++ · C
Stellar Core Protocol 23 Changes
Blockchain node audit · with Oak Security
- Cosmos SDK · Golang
DATA Network (Story Protocol) L1
Cosmos SDK chain audit · with Trust Security
- Rust · Solidity
Snowbridge
Cross-chain bridge audit · with Oak Security
- Golang · Cosmos SDK
Cosmos SDK
Cosmos SDK framework audit · with Oak Security
- Filecoin · Rust
Filecoin EVM (FEVM)
EVM implementation audit · with Oak Security
- Golang · Cosmos Hub
Cosmos Interchain Security
Cosmos SDK chain audit · with Oak Security
06 — Achievements
Achievements
08 — Contact